Showing posts with label Linux. Show all posts

Tuesday, May 03, 2005

Sguil on Gentoo

Finally, I can manage to install Sguil on Gentoo.From its website:
"Sguil (pronounced sgweel) is built by network security analysts for network security analysts. Sguil's main component is an intuitive GUI that provides realtime events from snort/barnyard. It also includes other components which facilitate the practice of Network Security Monitoring and event driven analysis of IDS alerts."

Basically, Sguil has 4 components:
- sensor, running snort IDS and using Barnyard to send the alert to database
- database, running mysql as central repository of all the alerts
- sguil server, connecting the client to sensors and as front-end interface for any SQL queries to database
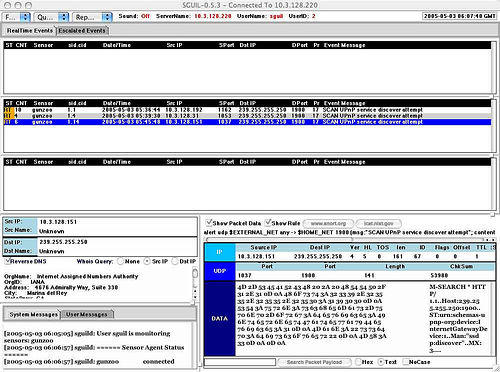
- sguil client, graphical front end interface for users which is very cool and can be used to chat within users as well!

Sguil now is considered the best monitoring tool for snort IDS. ACID is the alternative but it can't provide "real-time" alert as Sguil does, since ACID use web-based interface that needs to be refreshed all the time.


I won't write the step-by-step installation here, because the documentation is very clear.
I recommend to follow the instruction from Richard Bejtlijh in here.
The documentation is focused on the installation under freebsd. For Gentoo users, if you can't find the required packages in "emerge -s", then you have to download from the source.
Btw, my sguild is still not running TLS since I haven't yet found the tcltls source code.

For window$ client, follow the instruction how to install the client in here.
For Mac OS client:
- install X11
- install Tcl/Tk Agua
- download sguil client

If you don't modify the sguil.conf file, you will be connected to demo sguil server. Use 'sguil' for both username and password.
If you have setup your own server, just modify the "set SERVERHOST" parameter in the sguil.conf file.

Enjoy.

Friday, February 25, 2005

WRT54G Story Continues

Yesterday I bought another WRT54G from local store. After heavy bargaining and bluffing, I got it for $78. Now that I have 2 WRTs, I can put one at home for normal AP and one inside my car for “anything else”. Nice plan, huh?

From the outside box, there is no different between the new WRT and the one that I purchased couple of months ago. But after I removed it out from the box and read the version number on the back, it’s written “WRT54G v2.2”. My first WRT is v2.0.
I checked the box again and there is nothing at all that can give me a clue about the version of the device inside. Only I notice WRT54G v2.2 has serial number started from CDF7xxx while v2.0 has serial number CDF5xxx. But I’m not 100% sure.

Anyway, from our best friend Google I found out that there are currently 4 versions of WRT54G in the market:
v1.0, v1.1, v2.0 and v2.2.
Read the nice presentation from Neal Dudley here. It contains the pictures of all versions of WRT54G from external and internal view.

According to Simon in Linksysinfo forum, until now only the latest HyperWRT firmware and official firmware from Linksys can be used to flash v2.2. From somewhere I read that v2.2 actually uses the same Broadcom chipset, but now the LAN ports controller is part of the chipset.
Quick check from cpuinfo output confirms that both 2.0 and 2.2 versions are using the same chipset:
(none):[~]# cat /proc/cpuinfo
system type : Broadcom BCM947XX
processor : 0
cpu model : BCM3302 V0.7
BogoMIPS : 199.47

So now I’m stuck with WRT54G v2.2 and I can’t use my favorite Sveasoft Satori to flash the router. Should I use the new WRT as normal AP and the previous 2.0 as my mobile scanner? Well, I don’t like to spend 78 bucks only to get normal AP, so I downloaded the latest HyperWRT firmware and upgraded my new router.
Everything looks good. Now I have the option to increase the transmit power to 84 mW and I like the idea to put “reboot” button on the web interface. However, SSH is not available by default, only telnet. The good thing about HyperWRT is it has an option to modify the startup script. I put telnet command and “route add default gw 10.1.1.1” in startup script to make sure both will be available even I reboot the router. I don’t understand why there is no option to put default gateway for LAN interface on the web interface, even though I can achieve the same thing by putting the mentioned route command in startup script.

How about Kismet? Well, since there is no SSH, I have to run wget to get the kismet drone binary and config files. It consumes more effort since now I have to setup a web server with all the files. Sure it’s a linux system, honey. So I should be able to install any packages, right? The problem is the file system of HyperWRT is mounted as read only. We can write new files in /tmp directory only. And as you may guest, all these new files will go away once we reboot the router.

So I decide to try with “unofficial” Sveasoft Alchemy firmware which can be downloaded from freeWRT site. Hey listen, I don’t mind to pay $20 annually but I can’t pay with Paypal. I have sent Sveasoft support an email and requested to let me pay through other way.

The reason why I love Sveasoft software is because they build feature-rich firmware. I’m using Alchemy 6 Mod v16 and I can see there is an option to mount SMB file system. I haven’t tried to mount any drives yet but I believe it rocks!!!

How about the performance? I see that I can boost the power to 251 mW. Hmm, doesn’t it sound so tendentious?
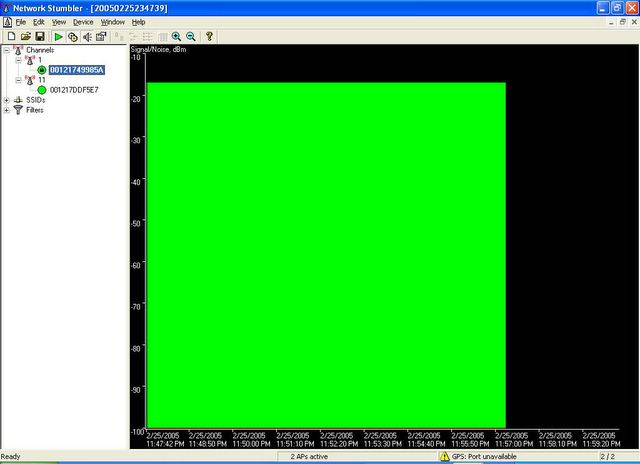
So I run netstumbler to verify. I put one Linksys in Channel 1 and the other in Channel 11. WRT54G v2.0 running Satori is on channel 1 with 28 mW Xmit power and the result can be seen below:


As we can see, the performance is constant in one point. Then I compare with WRT54G v2.2 running Alchemy on channel 11 with maximum 251 mW:


Well, the picture has spoken. The performance of Alchemy is not as stable as Satori. And even when I use WRT v2.2 Alchemy as normal AP, my laptop got disconnected several times.

I need to run more test to double check. But I believe I have already made my mind: Satori will stay at home and Alchemy will get the honour to be in my car. Unless it’s proven that I can’t use Alchemy to even run stable Kismet off course.

Is it true that we can use only HyperWRT and Sveasoft Alchemy for WRT54G v2.2? Some people say even you don’t turn the router into blue colored brick, there is a chance to lose the LAN ports if the firmware we use is not compatible with the new LAN controller chipset. Then you can re-flash the firmware only from the wireless network.

I would like to try it by myself, but not tonight.
OpenBSD Layer 2 bridging firewall has been waiting.
If you like to read the e-mail from Sveasoft to Google regarding the copyright violation by FreeWRT site, please check out this link. For me, I prefer to subscribe and get the firmware officially.
The decision is yours.

Wednesday, February 23, 2005

Kismet on WRT54G the Easiest Way

Linksys WRT54G is awesome.
It's an ADSL wireless router with linux-based software inside, licensed under GPL.
The price is reasonable, Amazon sells it for $60. I got mine from local store for about $80. The only drawback with WRT is it's not compatible with ADSL service offered by the only ISP in this country, Etisalat. But you know what? It means your chance to bargain the price is even better!
The most interesting feature from WRT is you can replace the software with third party firmware. Hey, it means we void the warranty! This is acceptable in the world where the only way to find the truth is by hacking. Suck the knowledge by testing and trying. Fill the brain with the answers of uncertainty.

Anyway, today we are going to make Linksys WRT54G as wireless IDS. This ADSL router will become the sensor or drone for famous wireless tool Kismet. As per its website, Kismet is an 802.11 layer2 wireless network detector, sniffer, and intrusion detection system. Kismet identifies networks by passively collecting packets and detecting standard named networks, detecting (and given time, decloaking) hidden networks, and infering the presence of nonbeaconing networks via data traffic.

There are several people that already have mentioned how we can run Kismet on WRT. From Rasmus’ Toys Page, RenderLab, Kismet forum, to Netstumbler discussion forum.
Just remember the following:
- WRT54G is only the drone, the sensor that collects wireless information. We need another computer or notebook running kismet server. Please don't run Micro$oft Window$ even it's possible, and we need to have SSH/SCP client as well
- When running kismet in WRT, we can’t use it as wireless access point at the same time
- All kismet files that we copy to WRT are kept temporarily in /tmp directory, and it will be flushed every time we reboot the device
- By doing this hack, there is a chance to ruin the router, screw the software and turn the device into blue colored brick, nice dual-antenna decoration for your living room … hmm, it’s worth $60, isn’t it?

Now, let's our adventure begins!
1. Read this blog until you understand what you are going to do.
2. If you are new to kismet, try to install it in your notebook and play around a bit to get familiar with the interface and configuration file.
3. Get the third party firmware. I’m using Sveasoft Satori-4.0 version firmware, so if you guys want to follow my steps, download it from Linksysinfo site. You must register but it’s free anyway. Btw, this is the last free version available from Sveasoft. To get the new version (alchemy) you need to donate $20 to them. But hey, $20 is nothing for cool firmware they produce. Unfortunately I can't subscribe since UAE is not in paypal country list.
4. Connect to WRT with your browser. Default IP address is 192.168.1.1, so type http://192.168.1.1 in your browser and put “admin” in password when prompted. You may change the IP address or your password as you wish. My WRT is using 10.1.1.10 IP address.
5. Replace linksys original software by going to Administration, Firmware Upgrade. Click browse and find the firmware, then push upgrade. If you are a religious man, start praying. Hopefully everything fine and you can complete the upgrade.
6. The router will reboot automatically and when it comes back you should see Satori-4.0 in Firmware Version.
7. Now go to Administration, Management and enable SSH.
8. We need to put our public key in Authorized Keys column. Assuming you are using Linux or *BSD with OpenSSH client in your notebook, generate the public-private key pairs:
[root@immortal ~]# ssh-keygen –t rsa

9. Grab the content of your public key from .ssh/id_rsa.pub file, and paste it in WRT's Authorized Keys.
10. Now you can SSH from your notebook to the router without putting any password.
11. Download the pre-compiled kismet drone binary from here. It’s bz2 file so you can decompress it using bz2 –d option, then untar the file by using tar –xvf option to get kismet folder.
12. Kismet folder contains /etc and /bin folder. We need to edit kismet_drone.conf file. In my case, for example, I modified the network in allowed host from default 192.168.0.0/16 to 10.0.0.0/8 network. Kismet server can connect to the drone from anywhere, as long as it still in “allowed host” scope. Btw, if you don’t know the meaning of /16 or /8, RTFM!
I assume my WRT54G is v2, since I don’t need to modify the source in kismet drone configuration file: source=wrt54g,eth1,wrt54g
13. Now we can upload the whole kismet folder to our WRT using scp:
[root@immortal ~]#scp –r kismet root@10.1.1.10:/tmp/kismet

Don’t forget to change the IP address according to your router address.
14. SSH to your WRT, and run the kismet drone:
(none):[~]# /tmp/kismet/bin/kismet_drone
Suid priv-dropping disabled. This may not be secure.
No specific sources given to be enabled, all will be enabled.
Enabling channel hopping.
Disabling channel splitting.
Source 0 (wrt54g): Enabling monitor mode for wrt54g source interface eth1 channel 6...
Source 0 (wrt54g): Opening wrt54g source interface eth1...
Kismet Drone 2004.04.devel_nikki_2004.05.23 (Kismet)
Listening on port 3501 (protocol 8).
Allowing connections from 10.0.0.0/255.0.0.0
WARNING: Setting driver in STA mode to enable channel hopping

Yes, it’s on, baby! Kismet drone is running and ready to accept the connection from kismet server on port 3501.
15. You need to run kismet server in your notebook. If you haven’t installed it, do so by compiling from source or type “emerge kismet” for Gentoo users.
We have to modify the kismet configuration file, /etc/kismet.conf by default, to use kismet drone as source:
source=kismet_drone,10.1.1.10:3501,drone

If you like kismet server to drop the privilege to normal user, put the username in suiduser configuration: suiduser=himawan

16. Change your working directory to any directory where the user that you specified in suiduser can write the kismet log files, then start kismet as root:
[root@immortal tmp]# kismet

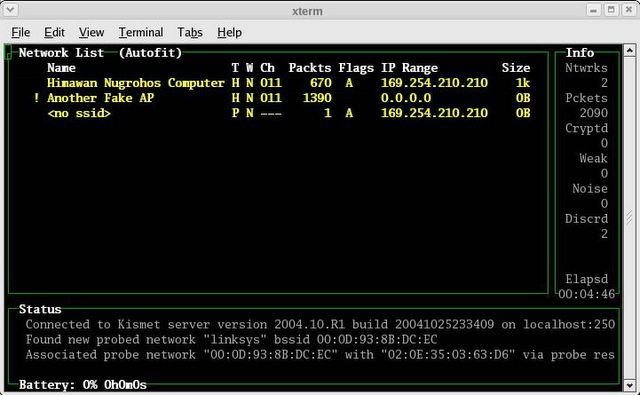
If everything’s ok, you should get the kismet panel interface just like below:


Well, it’s not difficult, isn’t it?
Just remember, every time you reboot WRT, you have to upload the kismet directory again using SCP.

Now what?
To make WRT54G running as real IDS, we have to analyze the log files in kismet server. Kismet will dump the wireless traffic its captured to Kismet-date.dump file. Then we can read the file using tcpdump –r option or ethereal. Or maybe test the traffic against snort rules?
I’ll check this later on. Now what I have in my mind is to use this router to do …
WARDRIVING!
Thursday, February 10, 2005

I'm in love

Today I'm in love.
Not to any female students in the University where I spend most of my time (have I mentioned that one of my biggest customers is American University? And my company signed the contract with them to put me dedicatedly as a network and security consultant).
I'm not falling in love to any secretaries in my office either.
But to OpenBSD. I'm in love with OpenBSD.
It's funny since I have been with OpenBSD from version 3.2. But I have never been using it for something useful other than as firewall to protect my home lab or PC labs in my office. Curse me!

Have you ever seen the movie where two best friends fall in love after several years of their friendship? They didn't have the feeling before, until one incident happened and clicked their mind?

It happened to me too. Couple of days ago I re-arranged my book shelf and found the Absolute OpenBSD book from Michael Lucas. I started reading the book and some strange feeling came to me. My hand was shaking, my heartbeat became faster and faster, I could hardly breathe... The book is so good and made it really hard for me to stop reading. OpenBSD rocks! How come I have just realized that OpenBSD is so beautiful after being with it for almost 2 years?
Easy to install yet provide minimum and secure default packages, BSD airtool for wireless auditing, BSD ports mechanism, scrubbing and bandwidth management, and nice T-shirts for only $20!
So since yesterday, I started installing this OS in several PCs. One will be my next NTP server, one will be my Squid server, and one installation in Sun hardware for testing. And btw, finally I received my Acer TravelMate notebook that I gave to my company for repair. It took them almost 2 months to fix it. Well the problem was only with the charger but with free repair cost I should not complaint, should I?

Now I'm trying to install Gentoo and OpenBSD in that notebook. I have finished the BSD part, and now waiting for my Gentoo stage 1 installation to build my base system. The objective is clear: dual-boot notebook with wireless tools in both OS.

Gento... is just like my first wife. And OpenBSD, is just like another girl I have a crush with after having couple of years marriage.
Thanks to you, Michael.

Hey, this post should be about configuring Cisco PIX Firewall.
The part where I should explain how people can connect to internal servers from the Internet. Well, after completing 3 blogs, several installation of OpenBSD, and about 9 hours Lord of The Rings DVDs non-stop, looks like the next thing I need to do is to hit my bed.
Until our next meeting...

Friday, January 28, 2005

Which OS?

I used to have about 10 computers at home. It was combination between 2 Pentium 4 machine, 3 Intel notebooks, 1 Sun Cobalt, 1 Ultra 5, 1 AMD Duron machine, 1 Powerbook G4 and 1 Pentium II box.
Well, I'm not trying to show off here, and anyway I have removed most of them. Currently I have 'only' IBM T42 notebook, 1 P4 machine, Powerbook G4, Sun Blade 100 and the Pentium II box.

Why should I have more than 1 machine?
Because I used to search for immortality, hunted down the uncertainty, tried to stay at bleeding-edge technology by installing several OS in different machines and test them.

And what's the conclusion?
For normal desktop, office work and multimedia, I believe Mac OS X is the best. Panther has very beautiful aqua interface and at the same time offers BSD console, so it won't stop me installing tcpdump, snort, hping and all tools I need to run everytime I get bored.
My powerbook stays as the multimedia center until I get the cute-looking MAC mini.
So this is the OS that I would give to my wife and kid. Beauty and virus-free.

For security stuff, including wireless, I decided to install Gentoo dual-boot with WinXP in my IBM. Hey, the XP comes with my T42, so I keep them to make sure I get the OS that I (must) purchased with the notebook. Micro$oft still gets my money anyway, so why should I throw their OS away?
And most of my customers are still running Windows, so I still need this OS to check particular client software or for WPA configuration testing, for example.
I made 2G FAT partition so I can share the files between OS. Yes, guys, I know that the current kernel even can support read-write NTFS partition. Just as precautions.

Gentoo is good to make me stay at bleeding-edge. I have two main purposes with Gentoo: penetration testing tools (including wireless wardriving stuff) and intrusion detection analysis. Later when my skill is appropriate I want to use it as forensic as well.
Meanwhile I keep my Blade running Snort IDS to monitor my small network and at the same time acts as a place to compile necessary testing exploits.

How about *BSD? Well, I use OpenBSD as firewall to protect my personal lab. I love PF very much and this powerful OS can live in my Pentium II machine. Try to run XP on that machine!

Personally I love Debian as well. I have been using Woody and one of Sarge-based distro, Xandros, for about a year without any complaints. I like knoppix-std too. Live CD is a good concept to distribute security tools knowledge without installing the OS.
My brain is limited, so I have to focus. I decided to stick with Gentoo. Especially since Gentoo allows me to build the system (almost) from scratch. Btw, I have tried Linux From Scratch as well :)

Is it enough? Unfortunately no.
Corporate customers still stick with big name and stable vendors. Here comes Sun Solaris and Red Hat Enterprise Linux. That's why I still have one machine running Fedora and currently downloading Sun Solaris 10 iso CDs. Sight...

But that's the beauty of life. Everything is so different. Diversity.
And one thing for sure: open-source is bliss.

Friday, January 21, 2005

Gentoo Sex

While bootsrapping my blade, I found an article how to fly with gentoo.

The article is good, but it's the quote in the end that killing me:
gentoo sex is updatedb; locate; talk; date; cd; strip; look; touch; finger; unzip; uptime; gawk; head; emerge --oneshot condom; mount; fsck; gasp; more; yes; yes; yes; more; umount; emerge -C condom; make clean; sleep

Heheh, I'm still trying to imagine the act.. drrrrrrrrrr!

Gentoo, everyone...?

I used to be a Red Hat user.
It all started when I was still in my university.
I had a hardcore-linux friend who taught me there is another OS than Micro$oft Window$.
Thanks to him, I spent my 50 bucks monthly living cost to purchase "Red Hat 4.2 Unleashed" book. Hey, back there in my country 50 bucks is more than enough for a student to live and still have fun.

Anyway, since few months ago I have decided to move to Gentoo.
Red Hat is no longer exist, leave its users like me with no choice: migrate to Fedora, or join Enterprise territory.
I choose to abandon them completely. No offense to community who shed their blood to continue developing Fedora, but the idea to provide free software at the beginning then start charging after people get used to it doesn't make sense to me at all.

So here I am now, staring at two monitors: 21-inch HP P1110 connected to Sun Blade 100, and 14-inch IBM T42 LCD display.
I'm doing Stage 1 installation on my Sun, and emerge -u world on my IBM. I keep the Window$ XP and IBM partition on my T42 though, just in case.

Some people say Gentoo is difficult to install. Well, I guess they are wrong. Gentoo community has put a lot of effort to make Gentoo Installation Handbook. Use it. RTFM. Google is your friend.

This is not my first installation. Perhaps, my 7th..or 8th? Gentoo power lies on its Portage. Once I get the system up and running, I don't need to worry about how to install new packages or upgrade my system. Just type the magic word: emerge.
Curious? Read the Gentoo Portage Introduction.
So what are you waiting for? Go to www.gentoo.org now and start reading the story of Larry the Cow. Enjoy.